EU.03.03.96
TERMS AND CONDITIONS FOR THE PROVISION OF SERVICES THROUGH THE ΜYRA PLATFORM
Effective Date 01.09.2026
1. Preamble
1.1 These terms and conditions (hereinafter referred to as the "Terms and Conditions") govern the provision of business information services by ICAP CRIF S.A., a company with registered seat in Kallithea (El. Venizelou 2, P.C. 17676), with VAT number 996952940, and G.E.M.I. number 147989301000 (hereinafter "ICAP CRIF") and a member of the CRIF group, to the Client. Upon acceptance of the Terms and Conditions by the Client, a binding agreement is created between the Client and ICAP CRIF (hereinafter "the Agreement").
1.2 ICAP CRIF, as part of its business activities, including the collection, processing, maintenance, organization and provision of business information services and commercial, financial and creditworthiness information relating to businesses and other counterparties, with the aim of promoting commercial credit and enhancing the reliability, transparency and security of transactions, provides the Client, through the MYRA platform, with products and/or services enabling access to information and data maintained in the ICAP CRIF business database ("ICAP CRIF Database") (the "Information"), subject to the terms and conditions of this Agreement.
1.3 The Client wishes to receive from ICAP CRIF and ICAP CRIF agrees to provide the Client information services with commercial and financial content on businesses in order to for the Client to assess its business risk, in accordance with the following terms and conditions:
2. Definitions
For the purposes of these Terms and Conditions, the following words and expressions shall have the following meanings, unless the text provides otherwise: "Permitted Purpose", unless otherwise specified in the Convention, means: a. the processing of information by the Client exclusively in the context of its lawful activity, for the achievement of its legitimate business purposes and the satisfaction of its legitimate interest, which consists of the exercise of the right of economic freedom on the basis of information that ensures commercial fidelity, reliability and security of transactions. b. the Client's corporate compliance with legislation relating to the prevention and suppression of money laundering (KYC, third party due diligence, beneficial owner, etc.) and terrorist financing, Law 5104/2024: Code of Tax Procedure, etc., through the "Business Family Tree" ("BFT") service as currently in force. "MYRA" is a modern Business Intelligence (BI) and Credit Risk Analysis platform. "Personal Data Protection Legislation" means any applicable legislation, including the General Data Protection Regulation (Regulation (EU) 2016/679) (hereinafter referred to as the "GDPR"), Law 4624/2019 as currently in force and in general the local data protection laws and regulations, opinions including guidelines and regulatory decisions of the local Data Protection Authority and all other applicable privacy laws. "Controller", "Data Subject", "Personal Data" and "Processing" will have the meaning attributed to them by the Data Protection Legislation.
3. Scope/Object
3.1 Through the MYRA platform, the Client may use Units purchased for the following services/products:
- Business Reports for companies, sectors and groups in Greece, Romania and Bulgaria.
- D&B Reports for companies outside Greece, Bulgaria, and Romania.
- Risk Analysis for the analysis and evaluation of credit risk in order to enable better risk management at the Client/partner level or centrally.
- Monitoring, for the continuous monitoring of the selected Client's portfolio through the receipt of automated notifications. The Client can additionally choose to enrich the analysis of the Client’s portfolio by uploading its own data for the companies included in it (e.g. Custom Score, Credit Analyst, Client Code, Outstanding Amount, etc.) hereinafter (Function "Upload Portfolio | Upload Your Data”).
3.2 With the BFT service, the Client has the opportunity to:
- Identify the interconnections between entities (Companies, Groups, Individuals).
- Identify the relationships between undertakings and natural persons exercising effective control or influence over the legal entity Information on the percentage of shares controlled by an entrepreneur.
- Reduce the risk of the business.
- Achieve transparency in partnerships.
- Audit the level of corporate compliance of the Client with legislation such as Law 4557/2018 on the prevention and suppression of money laundering (KYC, third party due diligence, beneficial owner, etc.) and terrorist financing, Law 5104/2024 Code of Tax Procedure, etc.
3.3 The Information is contained in the form of various types of product reports selected by the Client, as described on www.MYRA.icap.crif.com website (hereinafter referred to as the "Website") (clause 4.1).
4. Access and Use of Information
4.1 The Client will have access to the Information through the MYRA online platform, (https://myra.icap.crif.com/),or Website which extracts data from the ICAP CRIF Database. Access shall be effected by using a special access code and password, unique for each authorized user, who shall be indicated in the Payment Order/Order Form. The code and password ensure the confidentiality of transactions, the security of the system, and are exclusively used by the Client. The aforementioned code and password shall be provided by ICAP CRIF to the Client or to any employee thereof, duly authorized in writing for this purpose, in order to safeguard the confidentiality and security of the Information as well as complying with personal data provisions.
4.2 Subject to any different provisions of these Terms and Conditions and/or applicable law, the Client agrees that it will: only use the Information for the Permitted Purpose and in accordance with the Terms and Conditions and will ensure that all personnel using the Information are appropriately trained and qualified in such use. not sell, transfer, sub=license, distribute, commercially exploit, or otherwise make available to or use for the benefit of a third party, any of the Information beyond the Permitted Purpose and Terms and Conditions not copy, adapt, modify, reproduce, publish, alter, retransmit, edit or interfere in any way with the Information or combine it with other data unless expressly permitted under the Permitted Purpose or in accordance with current business practices agreed in writing by ICAP CRIF. not allow or proceed to any amendment, adaptation or other processing of the Information, whether or not specified in this term, without the prior written consent of ICAP CRIF.
4.3 Likewise, the Information may not be used before the courts in Greece or abroad, unless ICAP CRIF has granted its consent in writing, which consent may not be withheld unreasonably.
5. Payment Terms
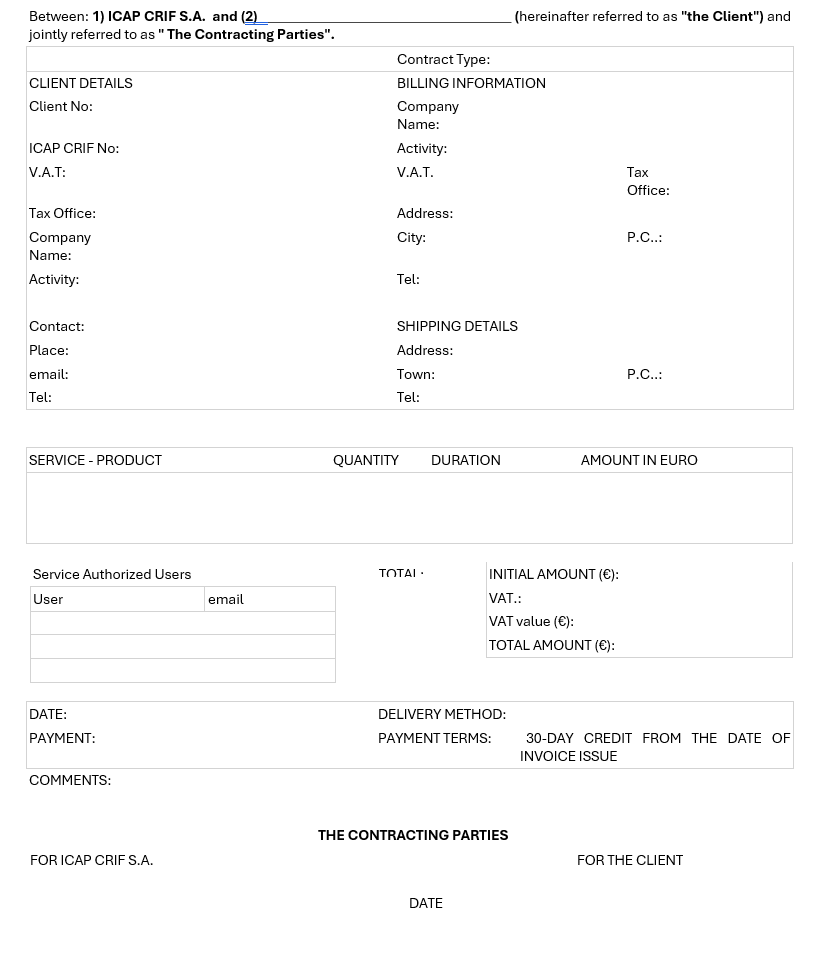
5.1 The fees of ICAP CRIF shall be determined in accordance with the service and/or product selected by the Client. In respect of each service to be provided by ICAP CRIF upon assignment by the Client, the Client and ICAP CRIF shall duly execute the relevant Payment Order/Order Form, which shall set out, at a minimum, the agreed services, the duration of the services, the applicable fees, as well as the method and due date of payment. A Sample Payment Order / Order Form is attached hereto as Annex 2.
5.2 Upon acceptance of the Terms and Conditions by the Client, ICAP CRIF shall issue an invoice to the Client, which shall be paid within thirty (30) days from the date of issuance.
5.3 In case payment via e-banking is selected, such payment will be made to any of ICAP CRIF’s bank accounts, as such are indicated on each invoice. Payment can also be made via PayPal using a credit or debit card.
5.4 In the event of late payment, unless the Client duly and reasonably disputes the relevant invoices ICAP CRIF may request late payment interest to be paid from the next day the invoice becomes overdue; such interest shall be calculated at the rate of the European Central Bank's base rate as applicable from time to time.
5.5 In case the Client receives the Information by using prepaid credit units, it is agreed that units consumed are not subject to refund or return, are consumed against the price of the products received by the Client and are valid for as long as indicated thereon.
5.6 Where the Client obtains Information through the units system (pre-purchased accounting units), it is agreed that such units are non-refundable, shall be consumed in accordance with the pricing of the products received by the Client, and shall be valid for the period indicated for each unit.
6. Duration – Termination
6.1 The duration of the Agreement for all services - products described in detail on the MYRA online platform, is set out in the Payment Order/Order Form. Upon its expiration, the Contract will be automatically renewed from year to year, unless either ICAP CRIF or the Client sends a written notice informing about the termination of the services provided, 30 days before the expiration date.
6.2 Each Party may terminate this Agreement for cause, following a prior 15-day notice. Such cause may indicatively be: Failure by the defaulting party to fulfil any contractual obligation following notice in writing and failure to comply with such obligation or remedy the situation within 15 days The defaulting party being unable to make payments or cease payments or otherwise intending to cease payments Ceasing of business activities of the defaulting party Bankruptcy of the defaulting party or entering thereof into a compulsory administration status, liquidation, receivership or any collective or not compulsory liquidation or foreclosure as well as in case of entering into a settlement agreement with creditors or any other similar situation.
6.3. In any case, ICAP CRIF shall be entitled to receive the remuneration agreed for services provided up until the date of termination.
7. Confidentiality and Personal Data
7.1 The Information relates to legal entities and is not considered as personal data according to article 4 of GDPR and therefore the provision of such Information does not fall within the provisions of the aforementioned Data Protection Legislation. The Client acknowledges and accepts that it shall not request and shall not receive Information containing personal data, and as such, the Data Protection Legislation is not applicable. However, the Client acknowledges and accepts that in case the Information contains personal data (sole proprietorships - natural persons - data subjects) the Data Protection Legislation is applicable.
7.2 When performing the "Upload Portfolio | Upload Your Data" in order to legitimize the processing of personal data by ICAP CRIF, the Client undertakes the obligation to designate ICAP CRIF as the processor pursuant to article 28.3 GDPR, in accordance with the " Controller- Processor Agreement", a draft of which is attached to these Terms and Conditions, as Annex 3.
7.3 In carrying out the other activities, the Contracting Parties will process the data as independent Data Controllers. The Contracting Parties undertake to comply with the data processing provisions of the GDPR and the applicable regulations and to use systems and procedures that comply with the provisions referred to in Article 32 of the GDPR. Whenever the Client needs to send personal data to ICAP CRIF in relation to which it acts as a Data Controller, the Client undertakes to provide an appropriate informative notice to the data subject concerned and guarantees that the processing of such personal data will be carried out on the basis of one or more of the legality conditions set out in Article 6 of the GDPR.
7.4 The Contracting Parties should take all appropriate measures to protect the rights, freedoms and legitimate interests of data subjects, as well as to ensure the transparency of the processing. In addition, the Contracting Parties are obliged to adopt all organizational and technical measures for the protection of personal data in order to ensure compliance with the terms of this Agreement and Data Protection Legislation.
7.5 Specifically for the BFT Service, the Client acknowledges and accepts that, if the Client requests to receive Information containing personal data of Clients, the Client’s suppliers or other persons connected to him/her, he/she will ensure, prior to the transmission of such information by ICAP CRIF, that the data subject has been informed: a) that under the legal conditions the Client will be a data subject for data relating to shareholdings in businesses; with the sole purpose of legally supporting the Client's legitimate interest, the Client's corporate compliance with the applicable regulatory framework (indicatively, Law 4557/2018 on the prevention and suppression of money laundering and terrorist financing, Law 5104/2024: Code of Tax Procedure, etc.) the consolidation of financial transactions in accordance with the provisions of applicable legislation, any decisions/instructions of the Greek Authority or any other competent body and the instructions of ICAP CRIF and b) for its rights, either in accordance with the applicable Greek provisions, or in accordance with articles 13-21 of the General Data Protection Regulation (EU) 2016/679.
7.6 In any case, ICAP CRIF, to satisfy the right of data subjects to be informed, publishes the necessary information to the public through its press and website, in accordance with Article 14(5)(b) of GDPR and/or through other appropriate ways and means.
7.7 Personal Data provided by ICAP CRIF to the Client under this Agreement may be used, for the execution of this Agreement, for complying with a regulatory obligation, as well as the fulfilment of the Client’s legitimate interests. To this extent, the Personal Data will be processed on the legal basis referred to, respectively, in Articles 6(1)(b), 6(1)(c) and 6(1)(f) of the GDPR but in any case the Client is solely responsible for processing the data received under this Agreement legitimately and for its general compliance with the Data Protection Legislation in force at the time.
7.8 The Client authorizes ICAP CRIF to appoint, in accordance with Art. 28, paragraph 2 of GDPR, all subjects authorised as subcontractors by the Client, as well as CRIF and other subcontractors that ICAP CRIF will use for the processing operations as other processors (hereinafter referred to as "Subcontractors").
7.9 ICAP CRIF will impose on all Subcontractors the same obligations regarding the protection of personal data that it undertakes towards the Client. Therefore, ICAP CRIF will provide Subcontractors with the same instructions given to it by the Client in accordance with Article 28.3 of GDPR.
7.10 Without prejudice to any terms providing otherwise in this Agreement and/or the legislation in force at the time the Client is obliged to treat the Information included in the products and services received by ICAP CRIF, entirely or partially, as well as any derivatives thereof, as private and confidential, ensure it is protected from an accidental or unlawful destruction, loss, alteration, prohibited transmission, as well as illegal processing of any kind, not make it available to third parties, with or without consideration, or disclose it to third parties in any way whatsoever, as such information is restricted to the “Permitted Purpose”. The Client shall adopt all necessary measures for the use of such Information only by respectively authorized employees, managers, partners, staff and/or agents, who shall be subject to privacy and confidentiality obligations with regards to the Information, by virtue of agreements in writing, including information on their obligations as per the Agreement and the law. Further, the Client is obliged to adopt all organizational and technical measures required, for the protection of Personal Data, in order to ensure compliance with the terms of the Agreement and the data privacy obligations. In case of unlawful processing of the Information, transferring of it to third parties or accidental loss, the Client shall indemnify ICAP CRIF according to clause 8.4.
7.11 ICAP CRIF may use the email and telephone contact details obtained in the context of its contractual relationship with the Client to directly promote similar products or services or to serve similar purposes, for satisfying Client’s legitimate interests (article 6 par. 1(f) of GDPR), unless the latter opposes to the use of said data for these purposes, either at the time of the execution of this Agreement, or at any time via email to privacy@icapcrif.com or via letter sent to ICAP CRIF S.A.’s address at 2, Eleftheriou Venizelou street, 17676, Kallithea, Attn: Data Controller.
7.12 ICAP CRIF applies appropriate and reasonable technical and organizational measures to ensure the confidentiality and protection of Personal Data against accidental or unlawful damage or accidental damage, modification, unauthorized disclosure, use or access. ICAP CRIF provides strict guidelines and through binding agreements requires any third parties, who may process personal data on its behalf to: (a) process them only for purposes consistent with ICAP CRIF’s processing purposes; and (b) implement appropriate technical and organizational measures for the protection of Personal Data. ICAP CRIF applies appropriate policies, procedures, controls and other measures that are necessary and allow it to demonstrate at all times that it processes Personal Data in accordance with its Privacy & Personal Data Protection Policy and the applicable Data Protection Legislation.
7.13 The Client acknowledges and accepts that personal data may be processed using electronic and automated means. In order to assist users in navigation and in the efficient use of the MYRA platform and reports, general-purpose AI models, pursuant to Chapter V of Regulation (EU) 2024/1689 (“AI Act”) and duly trained on the aforementioned platform and reports, will be used.
7.14 Termination, dissolution, or expiry of the Agreement shall not affect the validity and enforceability of Clause 7.
8. Liability of the Parties
8.1 The Client acknowledges that the Information, which includes commercial and financial data is indicative and provided exclusively for informative purposes for the entity under assessment. The provision of Information by ICAP CRIF shall in no case be conceived as an incentive or deterrent for the execution of a specific transaction, nor shall it constitute or be considered as advice to the Client by ICAP CRIF of a financial nature or any other kind whatsoever, as the Client makes its decision in the manner and based on the criteria the same determines.
8.2 The Client acknowledges that ICAP CRIF makes its best efforts to ensure the accuracy of Information and in general the proper implementation of this Agreement. To that end, ICAP CRIF relies to a great extent and on an ad hoc basis on information and records of third parties, which may not be updated or to declarations by the entities themselves, which may not be possible to be crosschecked for their accuracy. Further, the huge volume of data collected and the time required for processing thereof has as a result that it is likely that the Information is inaccurate or non-complete. The Client accepts the risk with regards to the quality, accuracy, evaluation or assessment of the Information.
8.3 ICAP CRIF will make all reasonable efforts to ensure the proper operation of its information systems and that access is uninterrupted and unhindered. In the event of a malfunction which is not due to Client’s fault, ICAP CRIF is required to restore without additional charge, its uninterrupted and smooth operation, in response to the Client’s relevant request, as the case may be, as indicated by the four Criticality Levels, set out in Annex 1.
8.4 The Contracting Parties are mutually responsible only for the proven direct damage of the other party, arising either from the contract hereof or from the law. The Contracting Parties explicitly exclude liability for damages and losses including any indirect and consequential losses, or other liabilities resulting from any acts or omissions due to actual or alleged infringement of this Agreement and of any applicable law. The Contracting Parties are not responsible for delays in fulfilling their obligations due to accidental events or force majeure. In addition, the Contracting Parties agree that ICAP CRIF’s liability is subject to the following limitations: i. ICAP CRIF’s obligation to indemnify the Client for proven direct damages may not exceed the amount paid by the Client to ICAP CRIF for the implementation of this Agreement to which it is hereby limited. The only exception to the limitation of the amount of compensation is the breach of Data Protection Legislation, in which case ICAP CRIF is required to indemnify the Client only for its proven direct damage. ii. Under no circumstances will ICAP CRIF be held liable for any kind of damage or loss suffered by any third party due to Client’s breach of the terms of the contract hereof and of any applicable law, including the Data Protection Legislation.
9. Ownership rights
9.1 The know-how, the way and methods of collection, rating, classification, evaluation, processing and presentation of the Information included in the products and services to be provided by ICAP CRIF, are owned by ICAP CRIF.
9.2 The Client is granted a personal, non-exclusive and non-transferable right to use the services and products received by ICAP CRIF in accordance with the terms of the Agreement.
10. Combatting corruption, bribery and money laundering
10.1 ICAP CRIF stands against any form of corruption and bribery, whether committed directly or indirectly through third parties/intermediaries. In relation to the performance of the services provided, the Parties undertake not to provide, directly or indirectly, any form of unfair benefit or other advantage to a natural or legal person of the private sector and/or the public sector for the ultimate purpose of securing or maintaining business activity and consequently must not accept any such benefit in exchange for or for the purpose of any preferential treatment related thereto and in any case in breach of applicable law, and to comply with laws and regulations on anti-corruption and bribery;
10.2 Parties expressly agree and declare that during the validity of these Terms and Conditions both Parties and their staff, will strictly comply with all applicable anti-money laundering laws in the country in which they operate, and will ensure that managers, employees, consultants, subsidiaries and affiliates and persons comply with these provisions and that they adopt generally accepted best practices to ensure compliance with these provisions.
11. General Terms
11.1 By using ICAP CRIF services - products, the Client is assumed to have reviewed and accepted the General Terms of Use of the website https://myra.icap.crif.com/terms-and-condition and the relevant Data Protection Policy https://www.icapcrif.com/privacy-policy/).
11.2. The Client acknowledges and agrees that it is solely responsible for periodically reviewing the ICAP CRIF’s website and Terms and Conditions for the provision of services through the MYRA platform, in order to remain informed of any amendments. Continued access to or use of the ICAP CRIF Website following the posting of such amendments shall constitute the Client’s full and unconditional acceptance of the amended terms.
11.3 The Parties may not assign the rights and obligations deriving from these Terms and Conditions to third parties.
11.4 The Terms and Conditions are governed by the laws of Greece. Any dispute which may arise from the execution or interpretation of the same shall be submitted to the competent courts of Athens, which shall have exclusive jurisdiction.
ANNEX 1
Technical Support based upon the following four Criticality Levels: Technical Support Based on Criticality Levels Support Availability Technical support is provided exclusively during business hours: Monday to Friday, 09:00–17:00 (EET, local time in Greece), excluding official public holidays. Any incident reported outside these hours or on public holidays will be considered as received at 09:00 on the next working day. All response and resolution times are calculated based on working hours only and in EET, regardless of the location of the support team.
Criticality Level: 1
- Effect on the system: Serious Impact
- Description: Inability to perform system functions that support the client's critical business activities, resulting in a critical impact on business operations.
- Response Time: Within 2 working hours, provided the issue is reported during the agreed support days and hours (Monday to Friday, 09:00–17:00 EET).
- Time for remediation plan: A temporary or final remediation plan, at the best reasonable effort considering the criticality and nature of the issue, will be provided to the Client within 8 working hours starting from the initial response.
Criticality Level: 2
- **Effect on the system: **Operating Degradation
- Description: System functions are available but with significant performance degradation.
- Response Time: Within 4 working hours, provided the issue is reported during the agreed support days and hours (Monday to Friday, 09:00–17:00 EET).
- Time for remediation plan: A temporary or final remediation plan, at the best reasonable effort considering the criticality and nature of the issue, will be provided to the Client within 24 working hours starting from the initial response.
Criticality Level: 3
- Effect on the system: The System is Functional
- Description: System functions are available with minor performance issues.
- Response Time: Within 24 working hours, provided the issue is reported during the agreed support days and hours (Monday to Friday, 09:00–17:00 EET).
- Time for remediation plan: A temporary or final remediation plan, at the best reasonable effort considering the criticality and nature of the issue, will be provided to the Client within 24 working hours starting from the initial response.
Criticality Level: 4
- **Effect on the system: **Superficial
- Description: Cosmetic issues or user interface inconveniences that do not affect core functionality.
- Response Time: Within 24 working hours, provided the issue is reported during the agreed support days and hours (Monday to Friday, 09:00–17:00 EET).
- Time for remediation plan: Not applicable. The fix of such issues will be prioritized and delivered through the regular release plan of the platform.
ANNEX 3 - Data Controller - Processor Agreement
Overview:
-
The company, ICAP CRIF S.A., with registered office at 2 El. Venizelou Street, Kallithea Attica (hereinafter "ICAP CRIF") provides the Client with the Upload Portfolio function | Upload Your Data, as defined in clause 7.2 of the "TERMS AND CONDITIONS OF PROVISION OF SERVICES THROUGH THE MYRA PLATFORM".
-
under the Upload Portfolio Service | Upload Your Data the Client can transmit personal data to ICAP CRIF in order to be able to perform it (and only for the Upload Portfolio | Upload Your Data), when such data does not fall under the special categories of data pursuant to Article 9 of the GDPR (hereinafter referred to as "Data"), on which the Client acts as a Data Controller, in accordance with the GDPR;
-
the activities carried out by ICAP CRIF under the Upload Portfolio function | Uploading Your Data on behalf of the Client also involves the processing of Data and requires the execution of specific tasks by ICAP CRIF, a company that has been selected for its experience, competence and reliability as the ideal company to ensure full compliance with existing personal data processing provisions, and which has also provided adequate assurances to implement adequate technical and organizational measures or which meet the requirements set out in the GDPR, ensuring the protection of the rights of data subjects. Taking into account the above, with this document, the Client
APPOINTS
in accordance with Article 28 of the GDPR, ICAP CRIF as
PROCESSOR
for the processing of Data in the context of the Upload Portfolio function | Upload Your Data (hereinafter referred to as "the Service") and for the diligent execution of the Terms and Conditions related to the aforementioned Service.
The Client (hereinafter the "Data Controller") assigns the following INSTRUCTIONS to ICAP CRIF (hereinafter the "Processor") and gives the following INSTRUCTIONS for data processing, which the Processor must follow:
(i) Data processing must be carried out by the Processor in full compliance with the applicable legislative provisions under the GDPR and any other applicable legislation, while taking into consideration the personal data protection measures introduced by the Romanian Data Protection Authority from time to time and concerning the processing performed by the Processor.
(ii) in carrying out its Data processing activities, the Processor can legitimately expect the Controller to guarantee that the Data sent as part of the diligent execution of the contract relating to the Service was collected by the Controller from the data subject or from third parties in compliance with all the requirements and on the basis of one or more assumptions of legitimacy required by the GDPR.
(iii) Data processing must be carried out by the Processor in its performance of the contract for the Service and for the purposes connected to providing the Service, as well as only for the time strictly necessary to achieve the aforementioned aims for the agreed contractual period and for the purposes strictly connected and instrumental to the management of related technical problems, and, in any case, in such a way as to guarantee the security and confidentiality of the Data; the processing may be carried out both manually and with the help of electronic means, or automatically and electronically.
(iv) the Data processed by the Processor as part of the Service shall not be disclosed to third parties, or circulated or transferred abroad, except where otherwise provided for in the contract and by the present letter of appointment; the Processor will not use the Data, either directly or indirectly, for purposes other than those related to the Service, and will not disclose the Data to third parties, except where required by law or by competent Judicial or Administrative Authorities.
(v) The Processor is authorized to use Sub- Processors in the normal performance of its services, as specified in the Contract. The Sub-Processors can process the Controller’s data only under the terms of the agreements in the relative “Appointment as Sub-Processor”. The appointment as Sub-Processor imposes the same rules on the protection and processing of personal data imposed by the Controller on the Processor under the applicable legislation, Agreement and this Data Controller - Processor Agreement. Furthermore, the Processor undertakes to inform the Controller regarding any changes and the addition or replacement of other Processors, to allow the Controller to oppose the changes. Within 10 days, the Controller can object to the new Sub-Processor by sending a written note to the Processor in which it explains the reasons for the objection, which must be objective, justified, and relating to the impossibility that the chosen Sub-Processor can guarantee data protection. If the Sub-Processors fail to comply with their data protection obligations, the Processor with assume full responsibility for the fulfillment of the obligations of the Sub-Processor with respect to the Controller. Annex A – List of authorized sub-processors.
(vi) The Processor can transfer the personal data subject to processing as provided by the Company outside the European Economic Area (EEA), including through its subcontractors. The Controller explicitly recognizes and accepts that, in the case that it does not consent to the transfer of data outside the European Economic Area or outside a jurisdiction declared adequate by the Decision of the European Commission, the Processor cannot provide the corresponding services and the Processor shall be completely indemnified from any associated consequences and shall not be liable in any way to the Controller for the fact that the Processor will not be able to the provide the Services subject to the Agreement. Furthermore, the Processor will provide the Controller with all the information necessary to allow any authorization to the transfer of data in relation to the Services. In the event of any transfer of data, the Processor will transfer the data based on the Adequacy Decision pursuant to art. 45 of the GDPR or through any data protection clauses adopted by the Commission pursuant to art. 46 of the GDPR.
(vii) on termination of the Service, the Processor must return the Data to the Controller on the basis of its instructions, or properly, completely, permanently and irreversibly delete the Data sent by the Controller for the performance of the Service and any existing copies, unless there is a legal obligation requiring the storage of personal data (viii) the Processor must identify in writing the Designated Employees for Data processing, who will be bound by a confidentiality agreement and suitably trained, as well as provide the Designated Employees with additional specific instructions, where necessary, in terms of what is set out in the legislation for the performance of the Data processing duties;
(ix) the Processor has the duty to comply with and ensure the Designated Employees comply with the provisions relating to Data security and, in particular, the Processor must adopt, in compliance with the provisions in art. 32 of the GDPR, the security measures required to ensure an appropriate level of security in relation to risk and be able to ensure the ongoing confidentiality, integrity and availability of the personal data being processed. These measures should minimize the risks, where identified, of loss or destruction of the Data, even if accidental, and of unauthorized access or Data processing without consent or not complying with the aim of the collection;
(x) the Processor must notify the Controller without unjustified delay and, in any case, not more than 48 hours from becoming aware of a data breach regarding data processed on behalf of the Controller. All the information concerning the event should be provided with this notification, and in any case at least: (i) a description of the nature of the personal data breach including, where possible, the categories and approximate number of data subjects concerned and the categories and approximate number of personal data records concerned; (ii) a description of the likely consequences of the personal data breach; and (iii) a description of the measures adopted or proposed measures to address the data breach and including, where appropriate, measures to mitigate its possible adverse effects. Where and to that extent that it is not possible to provide the information at the same time and the identification of the event, the information may be provided in phases without undue further delay;
(xi) the Processor undertakes to provide support to the Controller in the activities required to comply with the obligations of the latter in accordance with the GDPR, within the limits of the information it holds and of the processing performed on behalf of the Controller; (xii) The Processor keeps a record, pursuant to art. 30 paragraph 2 of the GDPR, in written and electronic form, of all categories of processing activities carried out on behalf of the Controller, containing: (i) the name and contact details of the Processor; (ii) the categories of processing carried out on behalf of the Controller; (iii) where applicable, transfers of personal data to a third country or an international organization, including the identification of that third country or international organization and, in the case of transfers referred to in the second subparagraph of Article 49, the documentation of suitable safeguards; and (iv) a general description of the technical and organizational security measures referred to in article 32 of the GDPR;
(xiii) the Controller can carry out sample checks at its own expense at the Processor's company offices, using personnel that have been expressly appointed to the task, by sending a prior request in writing to the Processor with advance notice of at least fifteen working days from the proposed date and, in any case, at the date and time to be agreed with the Processor, in order to assess compliance of the Data processing with the existing contract for the Service between the parties, with this letter of appointment, and the legislation in force. The Controller shall undertake to carry out the aforementioned verification activities in the shortest time possible - during office hours and on working days - so as not to disrupt the normal performance of the Processor's activities. The Processor undertakes to make available to the Controller all the information required to demonstrate compliance with the obligations assumed with the signing of the Contract and of this letter of appointment, and in general with the legislation applicable to the processing performed on behalf of the Controller; (xiv) if, as part of security measure checks, the Processor comes across shortcomings in relation to the security measures or any other aspect of the Data processing carried out as part of the Service which are the responsibility of the Controller, the Processor will immediately inform the Controller, who will quickly activate the appropriate internal departments in order to adopt the necessary actions
(xv) for the purposes of the regulation of responsibilities and related compensation rights in favor of the data subjects, the application of the provisions of art. 82 of the GDPR remains valid;
(xvi) in addition to what is set out above, the Processor should in any case carry out the Data processing for the Controller as part of the Service on the basis of the contract and the terms and conditions, and using the processing methods regulated therein, or which can be inferred from the contract and herein expressly incorporated by reference - where necessary - in addition to this letter of appointment, in terms of the tasks and instructions;
(xvii) the Processor can exercise any appropriate decision-making powers to enable the objectives of the law to be achieved and to implement the obligations and tasks specified above.
This contract is valid for the entire duration of the services /products provided, in accordance with the term i, therefore, upon their definitive termination this contract will expire at the same time with immediate effect, unless there are additional and independent circumstances justifying the continuation of the processing of the Data by the Processor in a limited manner and for a period limited to what is strictly necessary (for example, indicatively, in the case of abnormal events affecting the contractual relationship between the parties).
This agreement is binding and confidential and may not be disclosed or disclosed to third parties without the consent of the Data Controller, unless required by law or when ordered or requested by the competent authorities or for the purposes of legal defense or to assert a right of one of the Parties. By accepting the terms of this Agreement, the Processor accepts the assumption of its duties, under the conditions described above, confirms the direct and in-depth knowledge of the obligations it undertakes in relation to the text of the legislation and undertakes the obligation to carry out the processing of the Data in accordance with the instructions received from the Client.
Annex A
Authorized Sub-Processor-Subcontractor CRIF S.p.A., with its registered office at Via della Beverara, 21, Bologna, Italy, VAT number: 02083271201